

PhylaxGovernance and audit
Show any examiner exactly what your AI did.
Sign-in, secrets, policy and monitoring with one audit trail and the cost of every task.
We’ll spend 30 minutes with you on one of your workflows, and you don’t need to share any data.
Where Phylax works
Sets identity, secrets and policy, then watches the work against the protection rules for each kind of data, with attack tests and alerts (Phylax). These are the onboarding steps it works in, from your first decision to live work, and after go-live.
- Step 2 · Set upSet up sign-in and accessRemoves: AI on a shared or borrowed login.
- Step 7 · TestTest it, try to break it, fix itRemoves: “Trust us.”
- Step 9 · ShadowRun in shadow mode and prepare the teamRemoves: The leap of faith from test to live.
- After go-live · OperateOperate: watch, re-test, decideRemoves: Silent drift, and spend nobody can justify.
What Phylax does
Phylax is Inovagio’s trust layer: sign-in, secrets, policy and monitoring with one audit trail, from the screen to the disk.
Policy before and after
A policy engine checks every protected action before it runs and checks its result after.
One audit trail
Gateway, sign-in, agents and data write to the same hash-chained record, so one trail covers every step.
Your identity provider
Sign in with the identity provider you already use (single sign-on on every paid plan). Every action runs as a known person or service.
Cost per task
Monitoring shows what every task cost in models, compute and time.
Protection rules by kind of data
Each kind of data your work holds, such as personal, health or card data, has its own protection rules. Phylax checks them from shadow mode on, against the controls you map to your frameworks.
Watches the work after go-live
Off the request path, it reads the record of every step, spots results slipping from their baseline, runs attack tests and raises alerts, with kill rules for one Virtual Employee, a department or everything.
Phylax at work
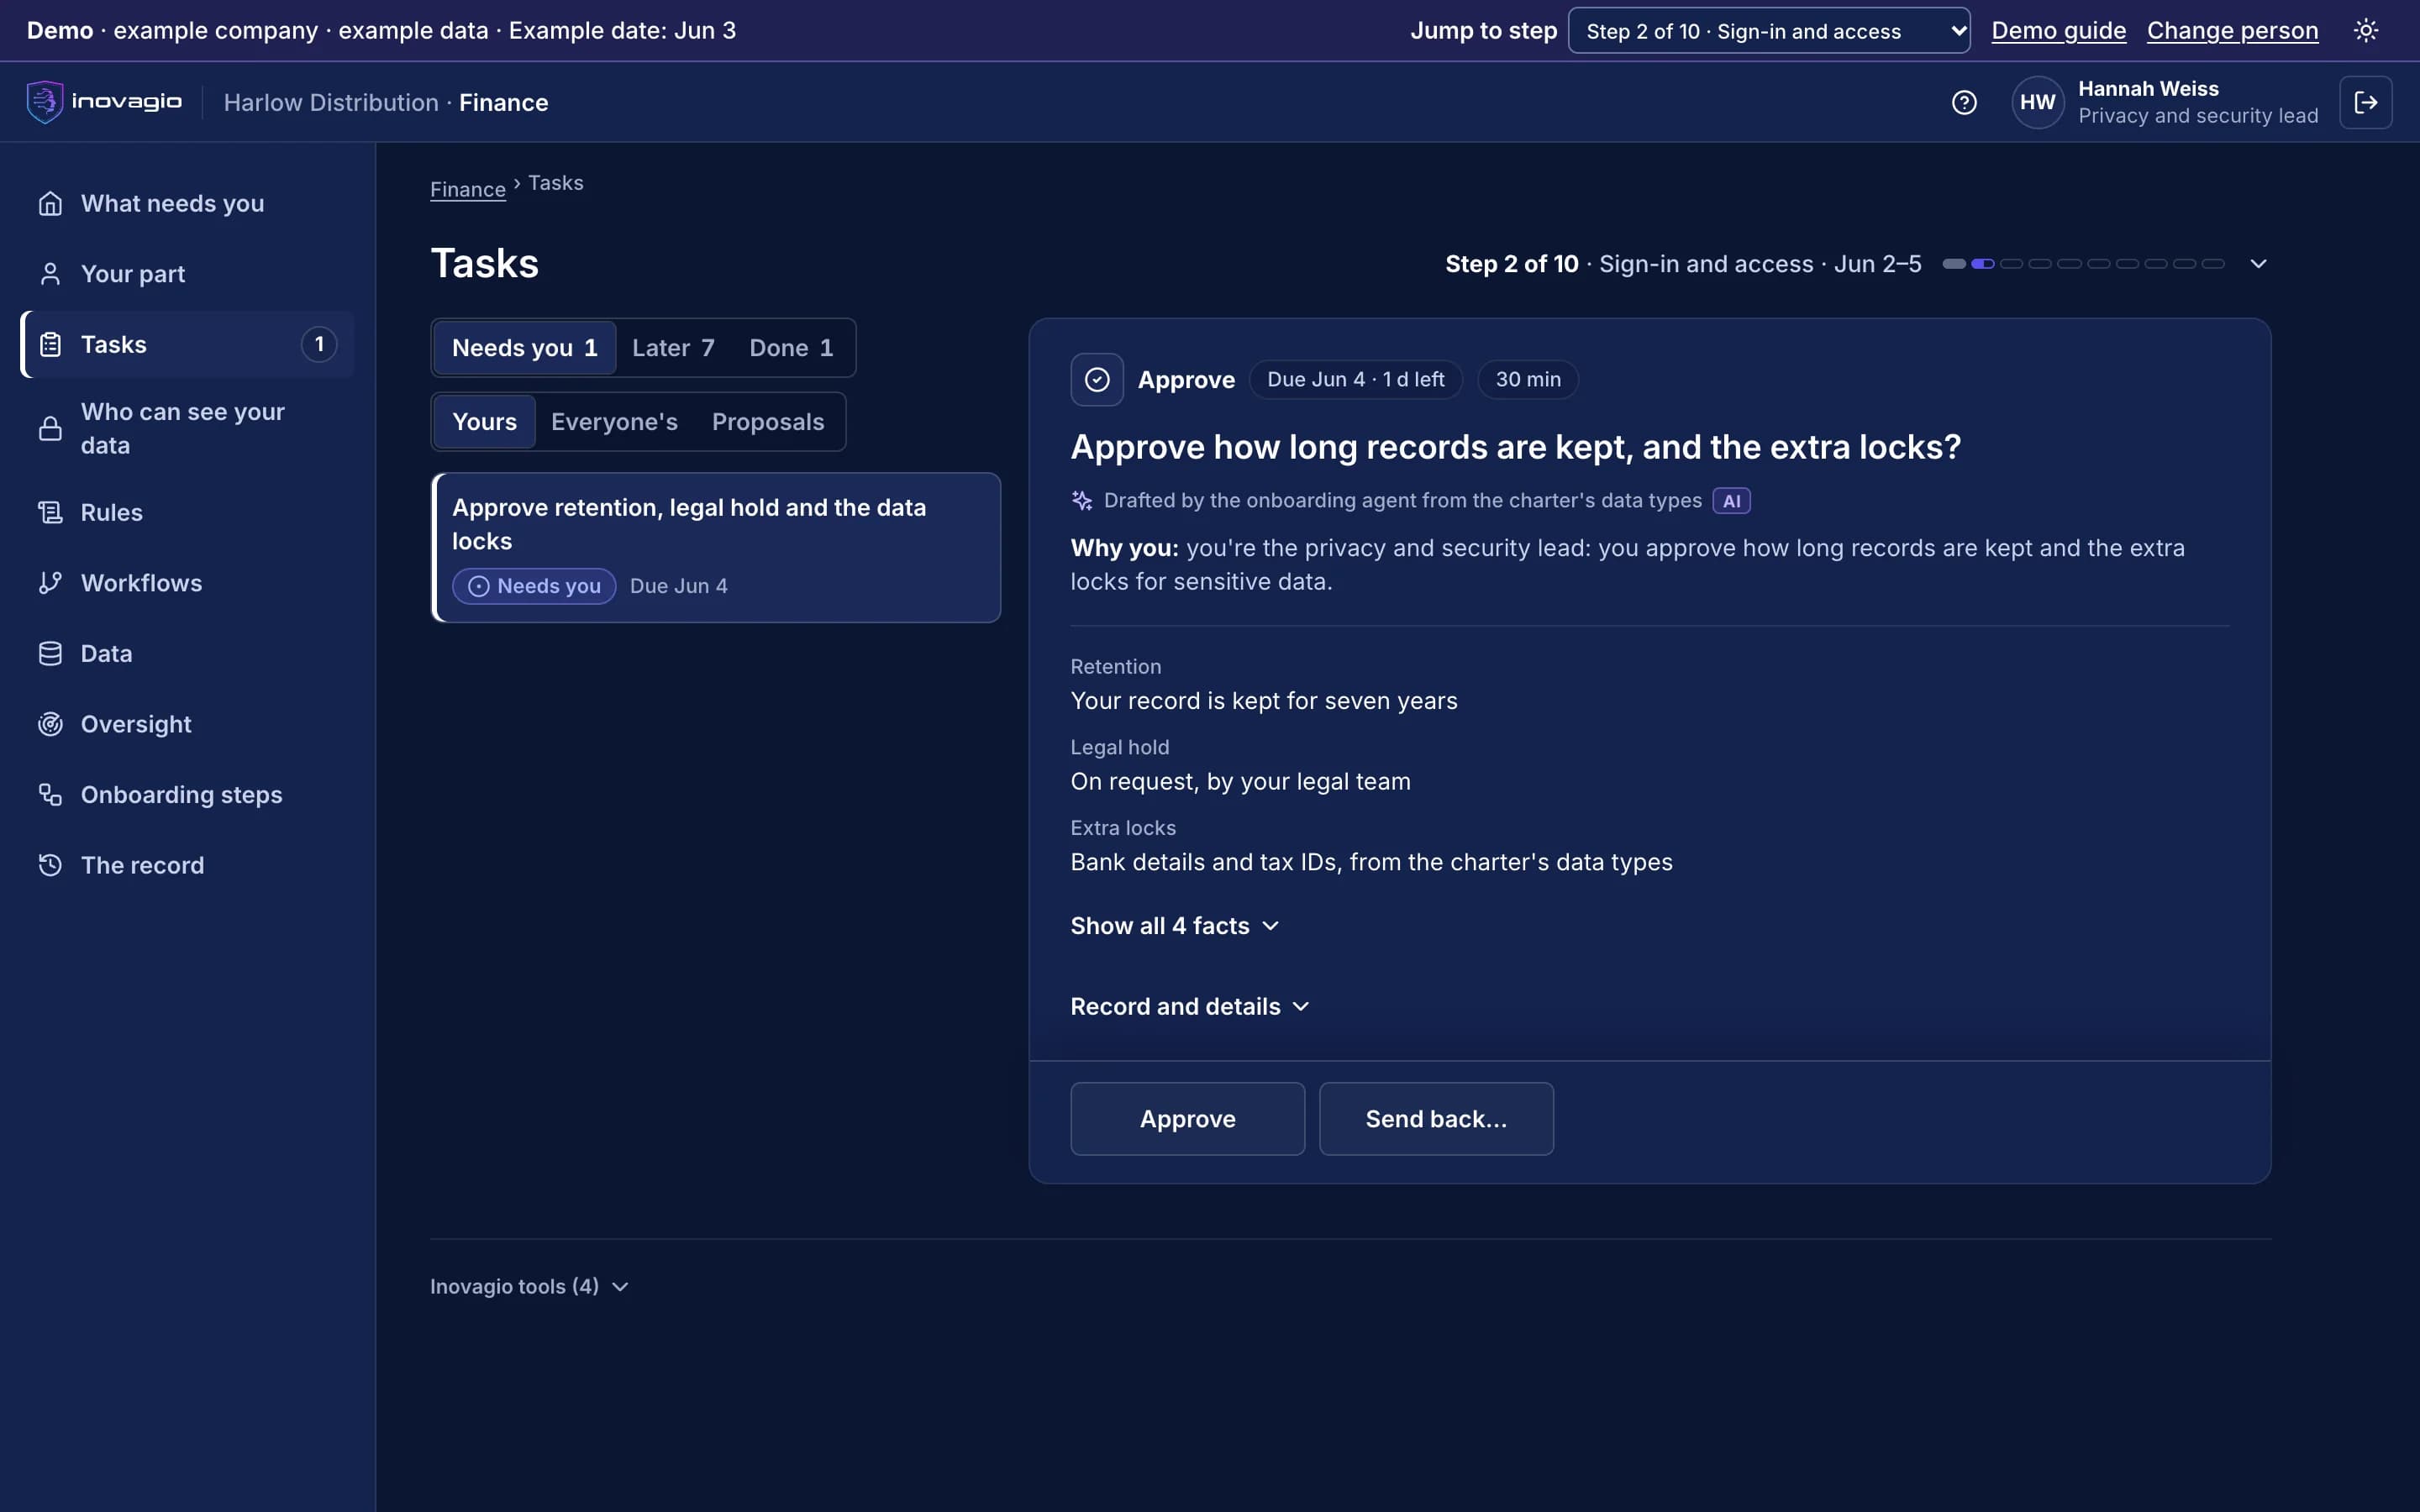
In the App at step 2: Set up sign-in and access.
- The record is kept for seven years.
- Legal hold on request, by your legal team.
- Extra locks for bank details and tax IDs, from the charter’s data types.
Inside Phylax
The views Phylax gives the people who run it, on sample data from Inovagio’s example companies.
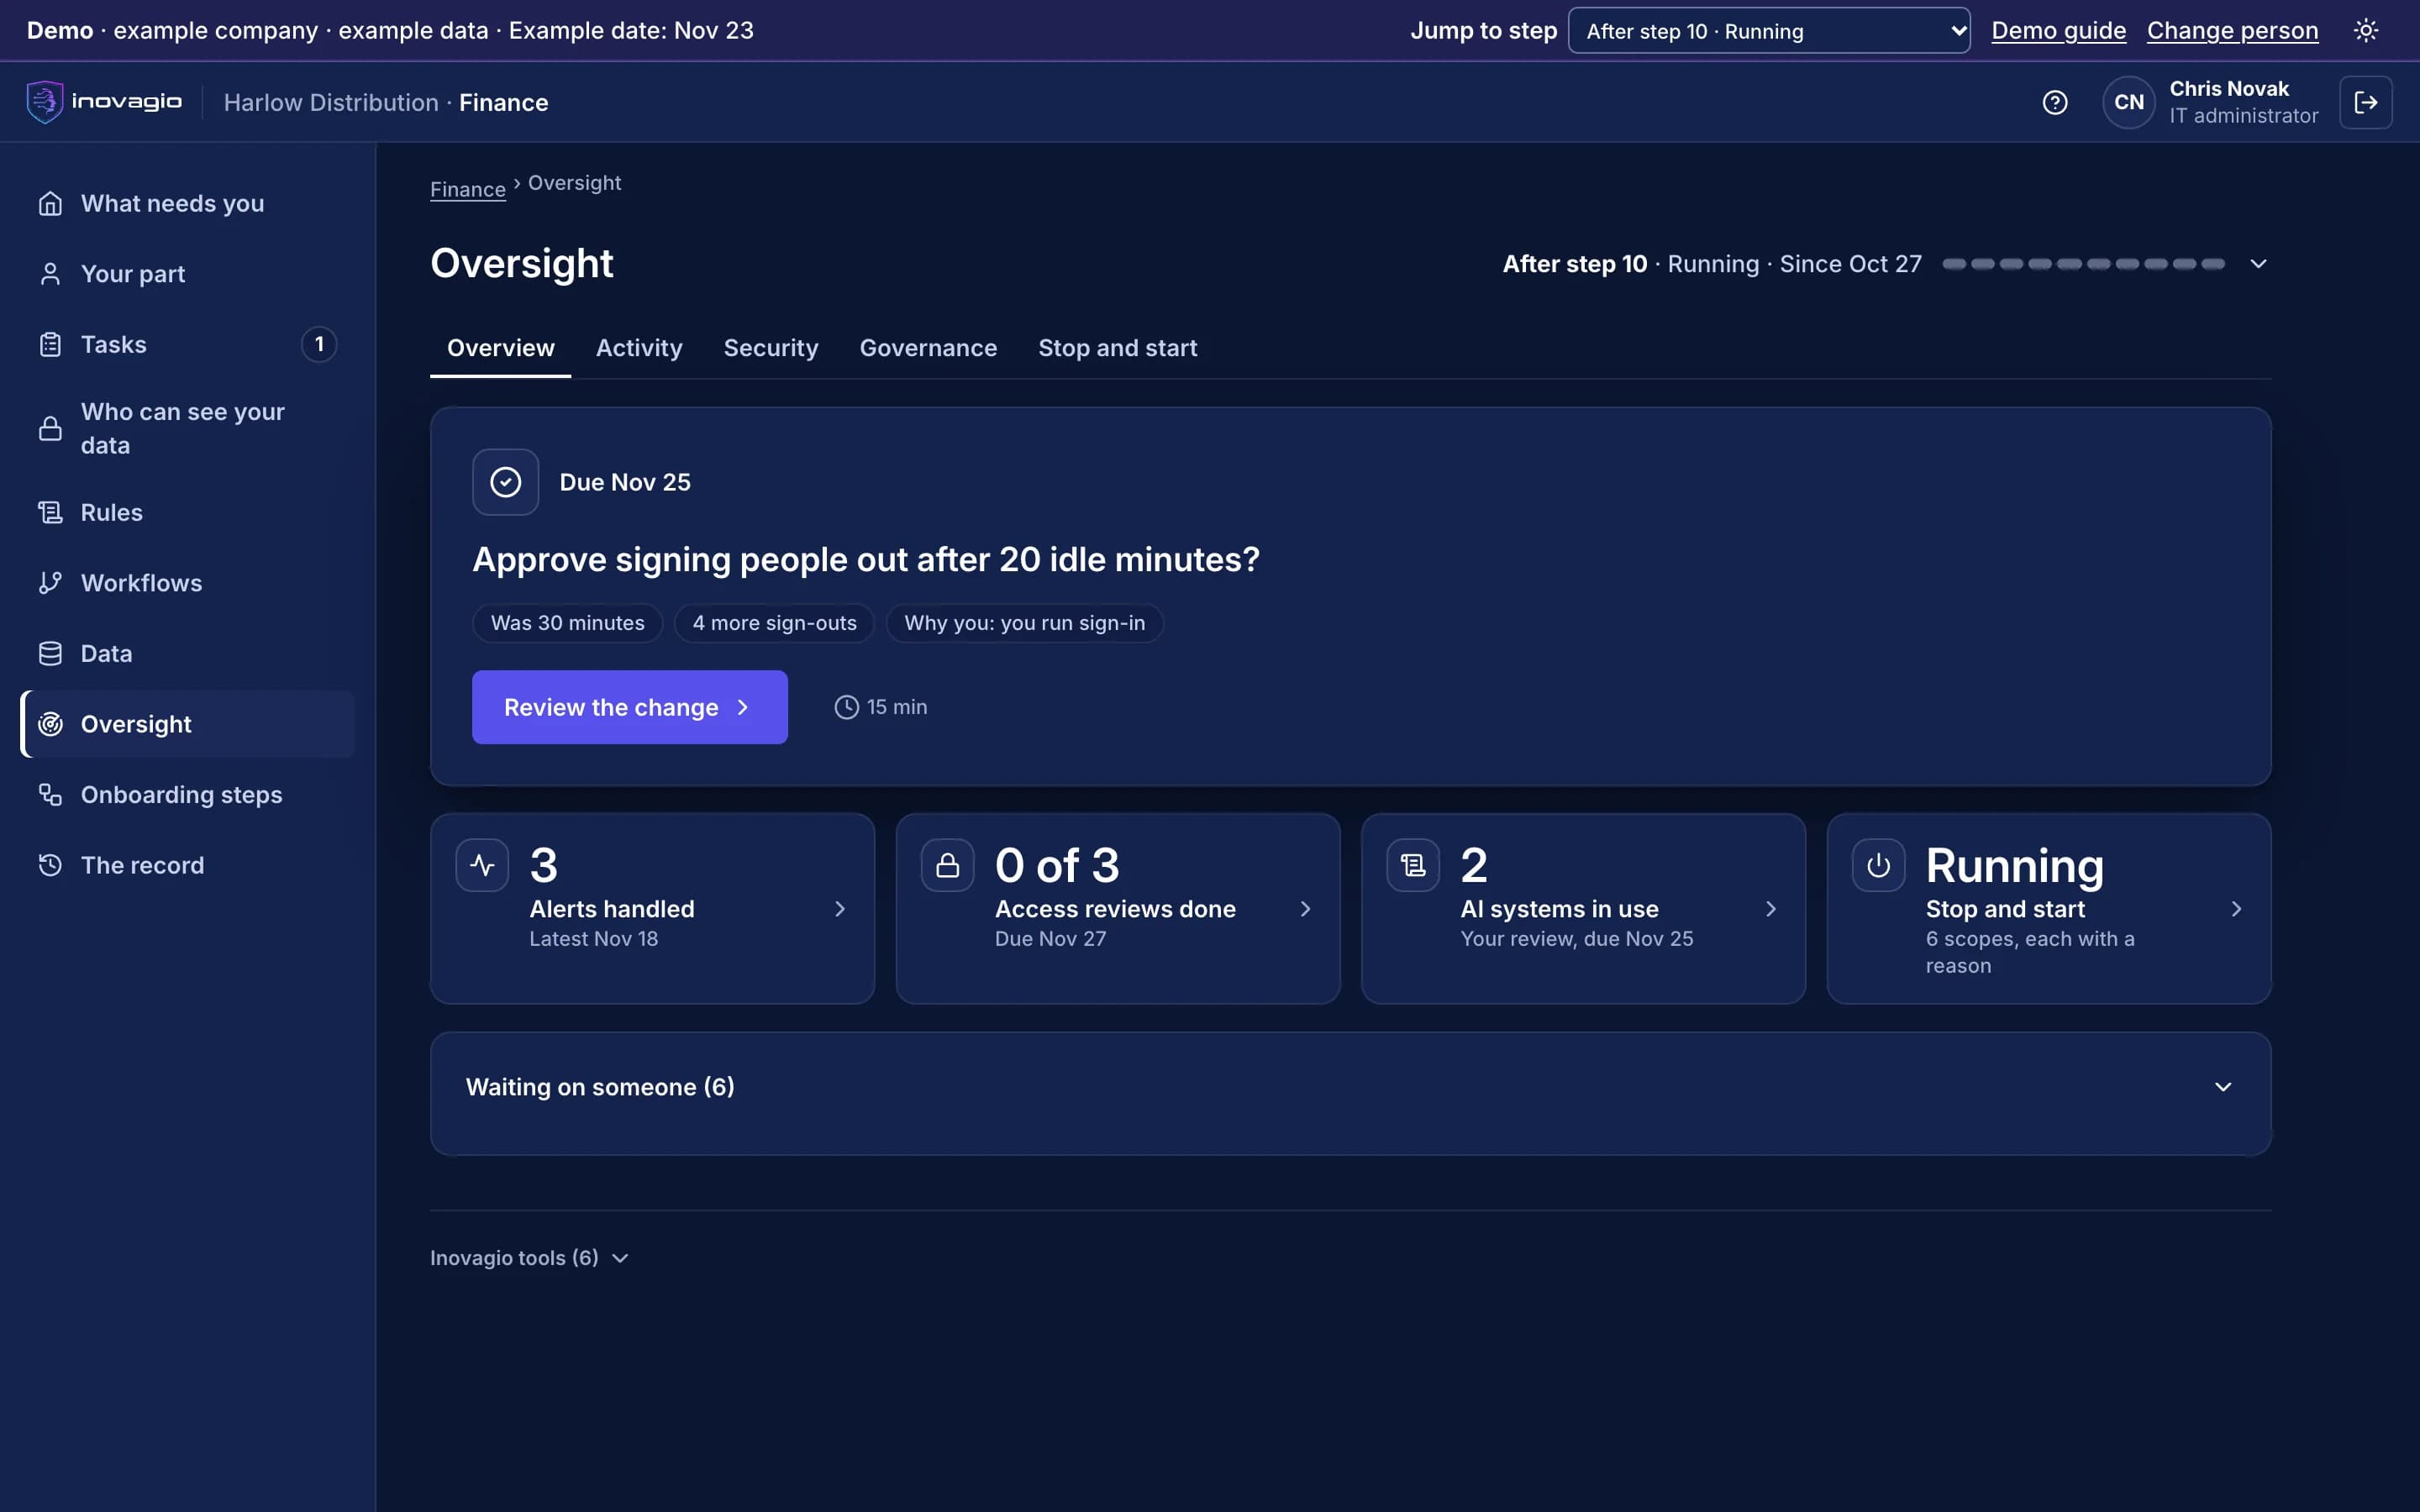
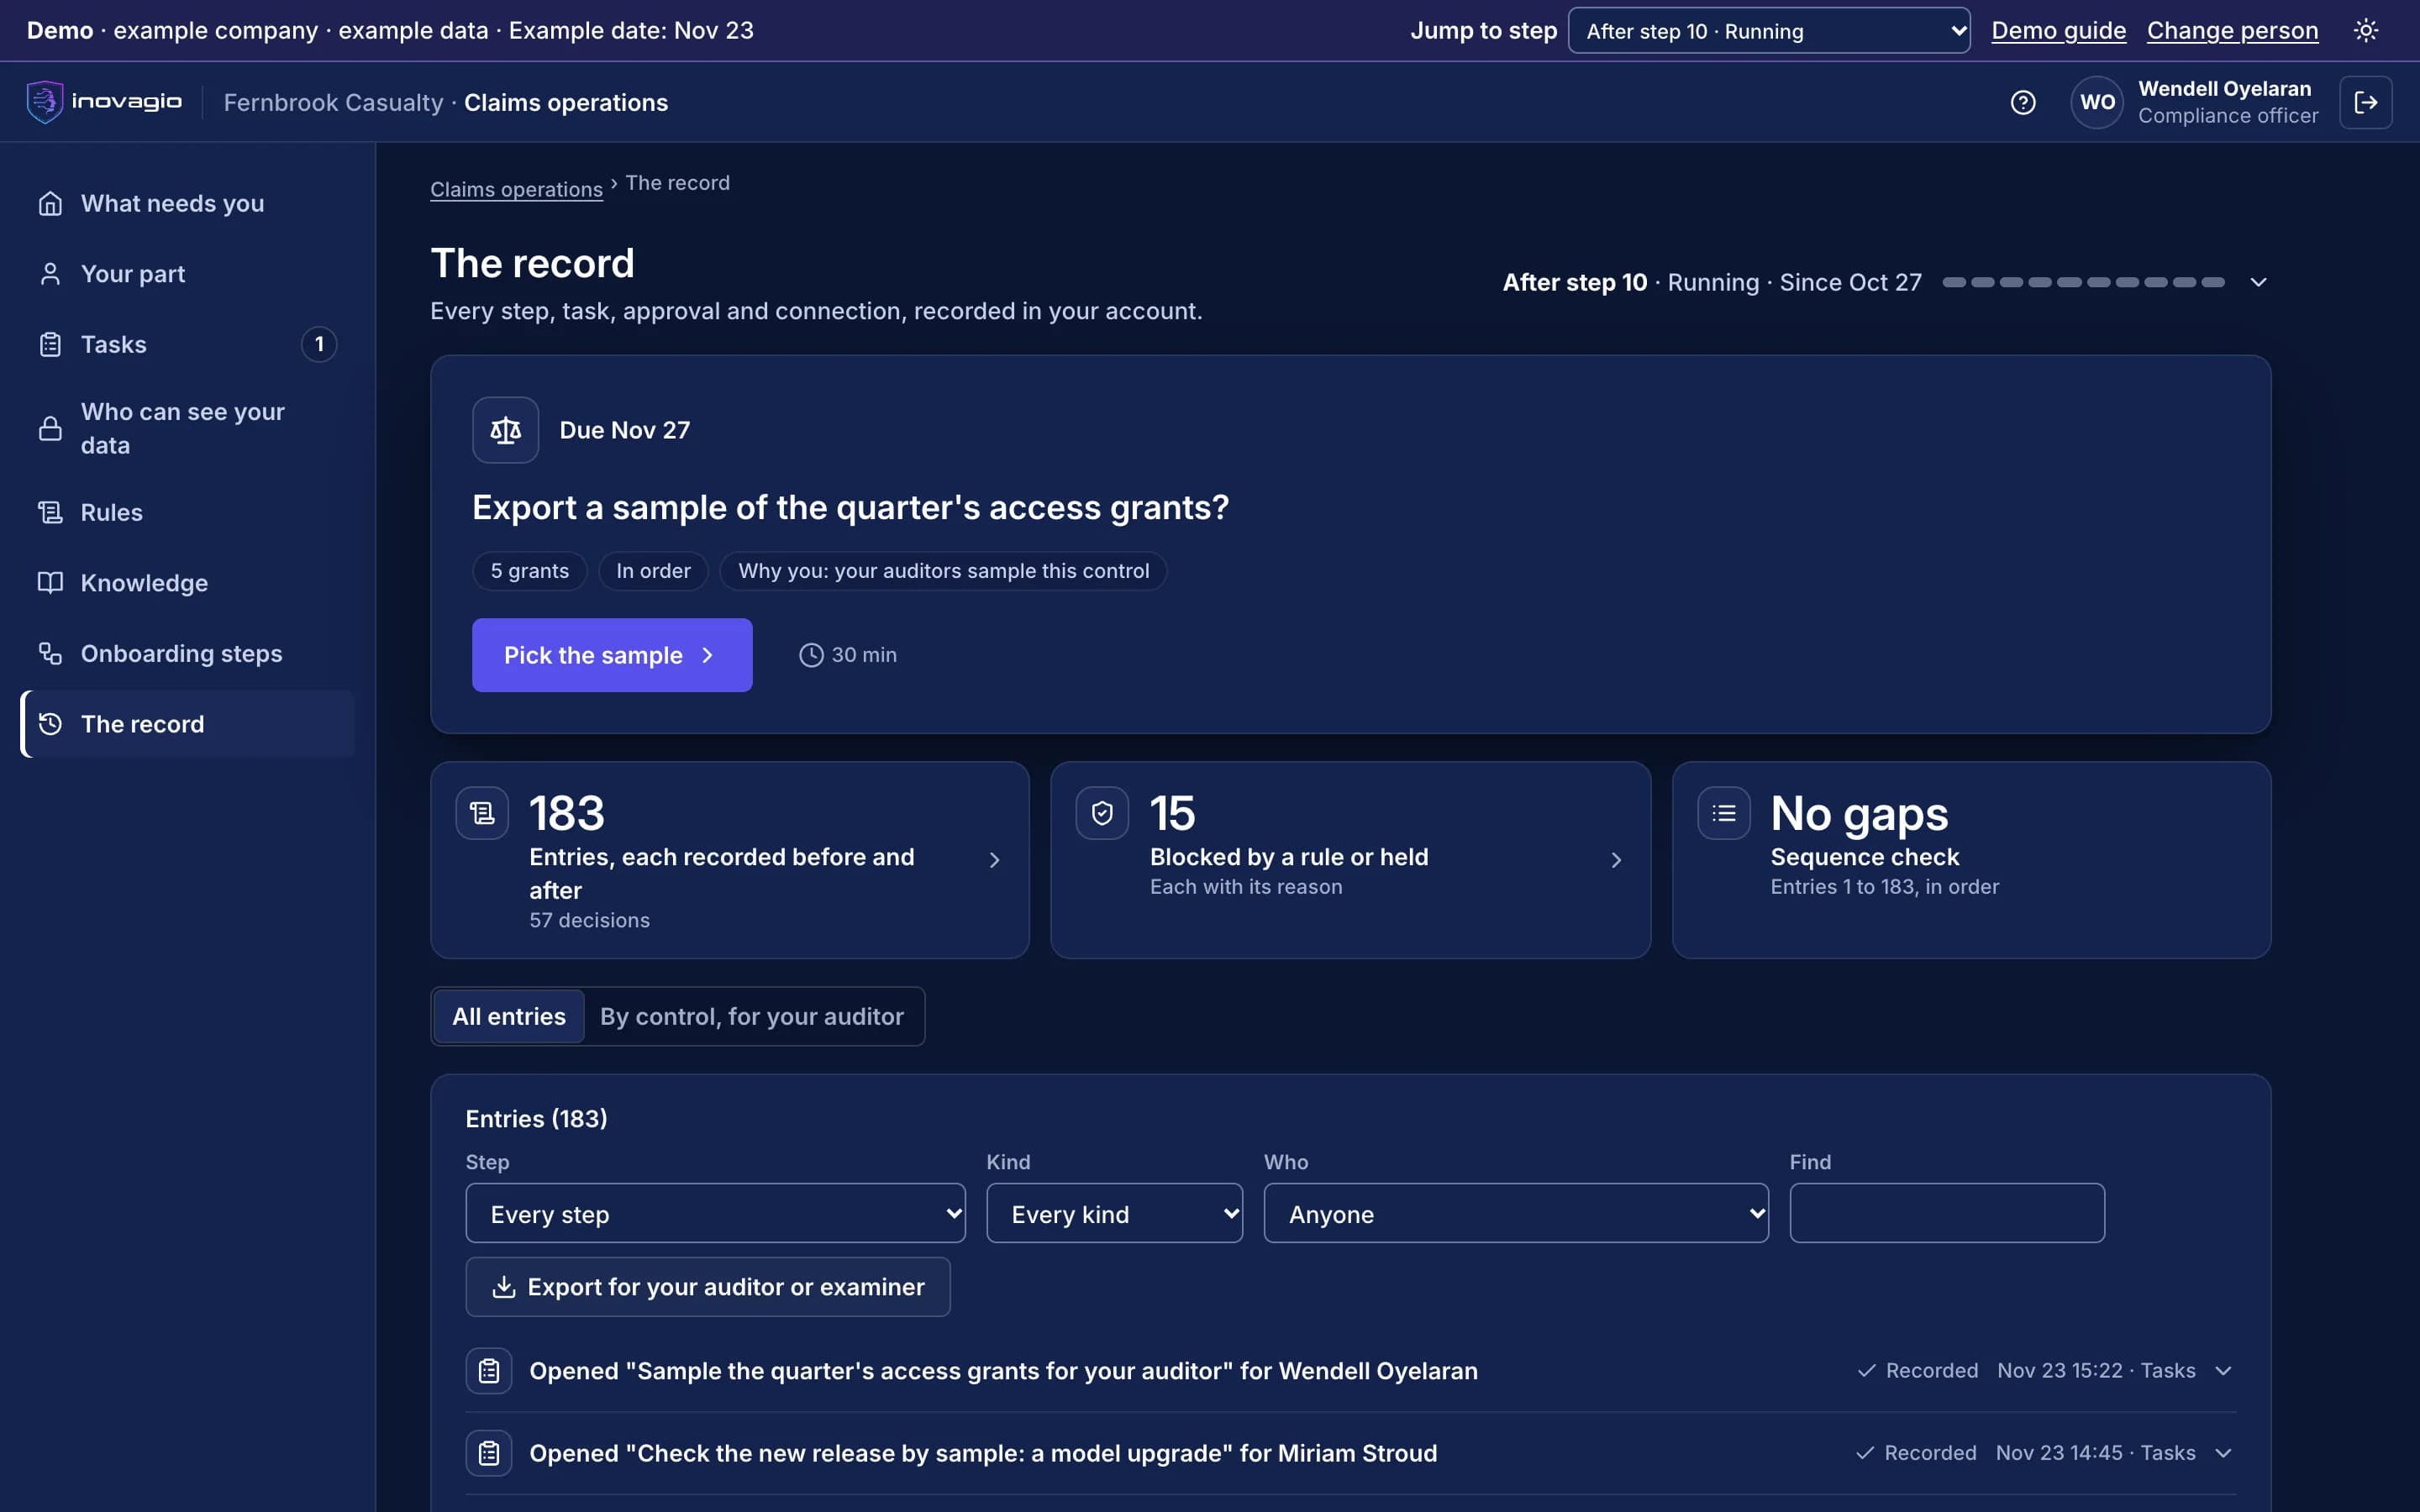
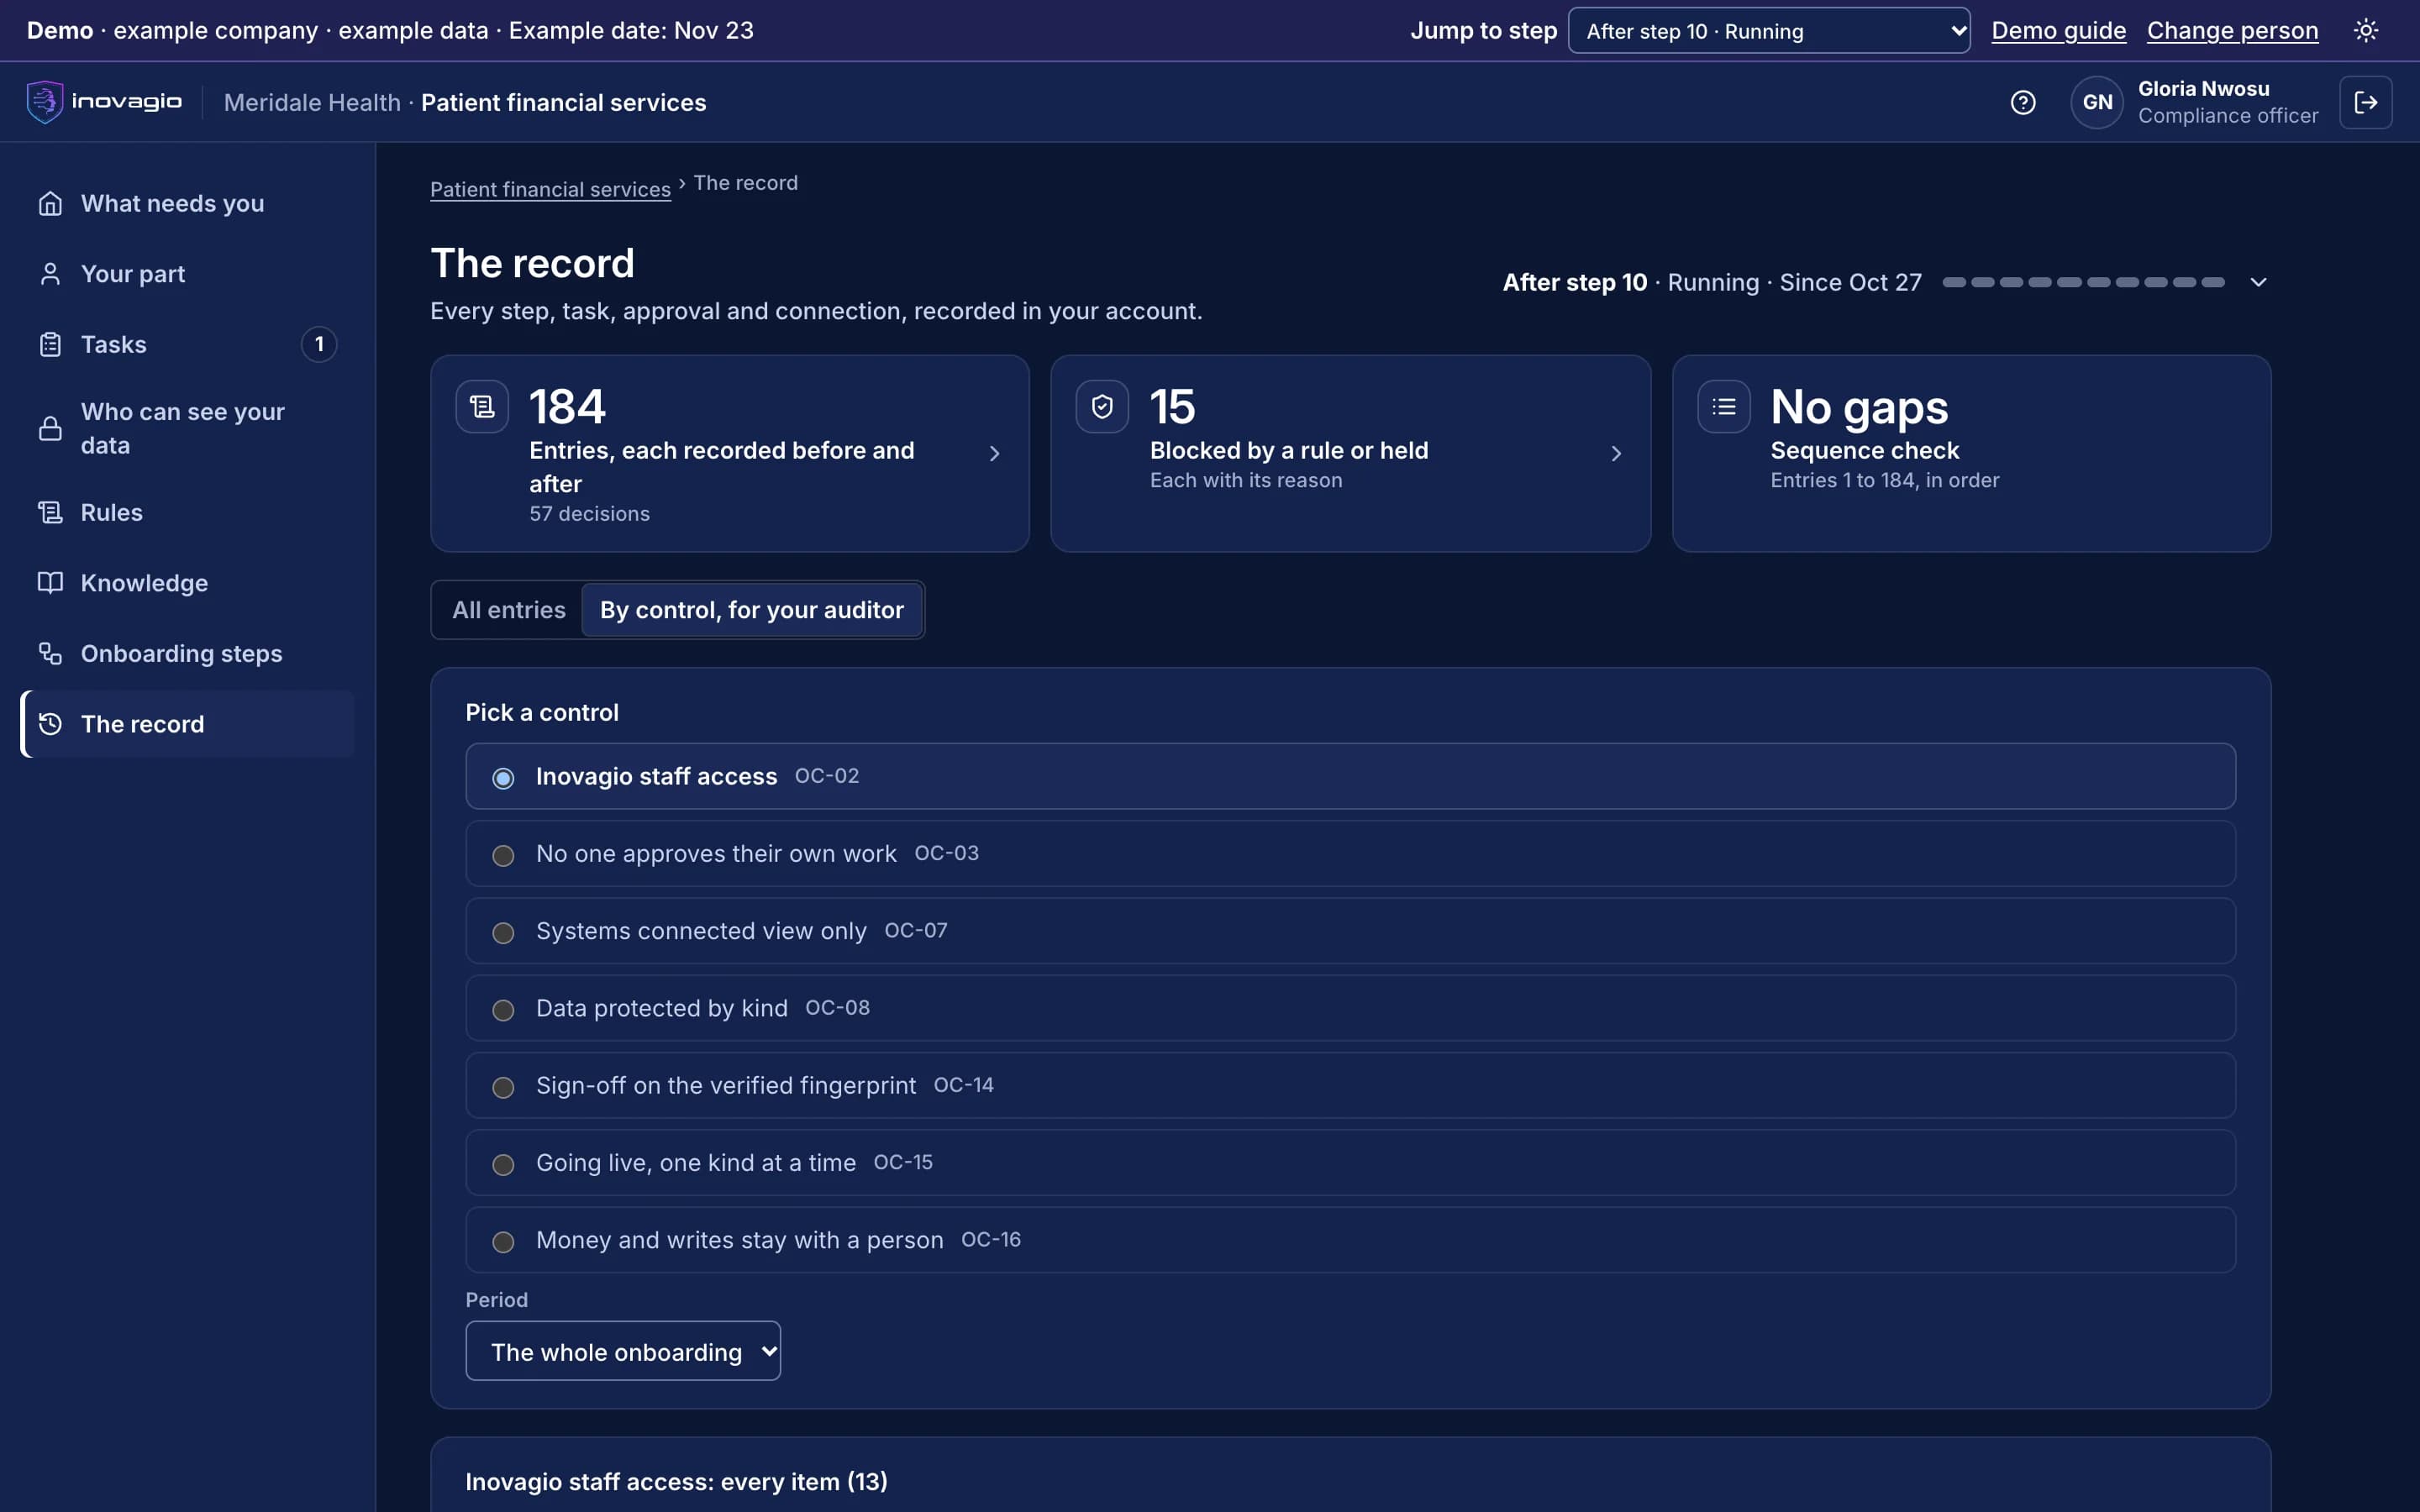
Phylax › Posture: the alerts handled, the access reviews, the AI systems in use and whether everything is running, with the next decision. Sample data from Inovagio’s example companies.
The products that make up Phylax.
Phylax
- AuthIdentity and sign-inOne sign-in for every person, service and AI agent.
- Inovagio SecretsSecrets and keysKeep every credential sealed, scoped and rotated.
- GuardAI safetyContent safety on every prompt, response and tool call.
What you get with Phylax
Security controls
Gateway, identity, secrets and monitoring in one control layer, built into the platform.
Audit
One tamper-evident trail from the screen to the disk.
AI policy
Your written policy, enforced as rules on every action.
AI spend
Cost per task, shown as it happens.
Everything Phylax does, by area.
Policy and authorization
- Role-based permission catalog checked on every protected operation
- Tenant isolation enforced before role checks
- Prebuilt control profiles for common regulatory frameworks
- Consent management
- Segregation of duties on approvals
- Agent actions attributed to the person they act for
Human approvals
- Durable approval inbox for operators and reviewers
- Defer, escalate and timeout policies
- Multi-party approval thresholds
- No self-approval
- Queryable decision history for auditors and resumed runs
- A denial is marked human-confirmed only when a person denied it
Audit and evidence
- SHA-256 hash-chained audit trail with chain verification
- Signed run receipts with cost and latency attribution
- Audit collection and aggregation across services
- Audit report and self-assessment generation
- Evidence for the AI regulations you report against
Monitoring and response
- Continuous control monitoring
- Behavioral baselines and anomaly detection for agents
- Automated red-team evaluation runs
- Canary sandbox for risky changes
- Incident playbooks and an incident mode
- Alert routing with deduplication
- Kill rules for one Virtual Employee, a department or everything
What Phylax replaces
Phylax does the work of these, inside one platform with one identity, one policy and one record:
- Policy documents enforced by hand
- Approval workflows run in email and chat
- Audit logs stitched together from separate tools
- Compliance evidence kept in spreadsheets
- Separate incident tooling for AI agents
The controls Phylax brings
Every Inovagio product keeps the same five commitments, because regulated work needs all five at once.
Security
Policy is checked before and after every protected action.
Governance
Approvals, roles and rules in one place, enforced in the runtime.
On the record
A tamper-evident trail you can replay for an auditor.
Monitoring
Policy decisions and approvals appear in Panoptes alongside operations.
Cost per task
The cost of every governed task is recorded with its decision.
Phylax in your industry
Every industry runs the same ten steps, so Phylax does the same job in each, on that industry’s own work.
- Financial servicesBanks, credit unions, lenders and insurersWorked example: Alder Ridge Community Bank · Example company
- Healthcare providersHealth systems, hospitals and physician groupsWorked example: Meridale Health · Example company
- Health plansMedicare Advantage, Medicaid and commercial plansWorked example: Ashgrove Health Plan · Example company
- LegalLaw firms and in-house legal teamsWorked example: Calloway Finch · Example company
- GovernmentState, county and city agenciesWorked example: City of Larkhaven · Example company
- DefenseDefense contractors and their suppliersWorked example: Keelstone Aerospace · Example company
- Finance operationsFinance teams in any industry
For developers: Phylax at a glance
- Frameworks
- Control mappings for the regulatory frameworks you report against
- Audit integrity
- SHA-256 hash chain; signed run receipts
- Inputs
- The platform audit trail and OpenTelemetry stream, read from Panoptes' telemetry store with Phylax’s own credential
- Outputs
- Alerts as OpenTelemetry logs (severity, control, evidence reference); kill requests to Guard
- Interfaces
- Alerts and control status through an API, read with the caller’s own permissions
- Runtime
- Supervised service off the request path
- Platforms
- macOS, Linux and Windows servers
Phylax in the platform.
Where Phylax fits
One platformAgent HarnessAgent harness
Inovagio CLIInovagio DesktopWeb ChatInovagio SDK
OpsisExperience layer
FolioMorphe
Virtual EmployeesVirtual Employee layer
NexusErgon
SynesisKnowledge layer
PerceptionMNEMOS
OriginModel layer
Inference ServerForge
Phylax (this layer)Trust layer
AuthInovagio SecretsGuard
OperationsOperations
PanoptesArchon
Platform servicesPlatform services
ServerAPI ManagementConnect
Questions
Phylax questions
How does Phylax support an AI governance program?
It turns your written policy into enforced rules, records every decision and approval, and lets you replay any task for an examiner.
Does tenant isolation depend on how it is deployed?
No. The signed-in identity’s tenant binds every resource and key in code, whatever the deployment.
Guides and posts on Phylax
 Guide · GovernanceABA Formal Opinion 512: an AI checklist for law firmsABA Formal Opinion 512 applies the duties lawyers already have to generative AI. This guide turns competence, confidentiality, client communication, supervision and fees into questions a firm can answer, and lists what to ask of any AI tool before client work goes near it. · 5 min read
 Guide · GovernanceAI agents and CUI: keeping controlled information controlledThe federal rules for controlled unclassified information say who may see it, where it is kept and when it may be shared. An AI agent that reads a drawing or drafts a supplier letter has to follow them too. This guide covers what the rules ask and how to set up an agent that follows them. · 5 min read
 Article · GovernanceAI in a market conduct exam: what insurers get askedA state insurance department can ask about any AI system that makes or supports decisions affecting consumers, in an investigation or a market conduct exam. This post covers what the NAIC model bulletin says examiners may request, and how to have each answer ready before the letter arrives. · 5 min read
 Article · GovernanceAI in Medicare Advantage coverage decisions: what CMS allowsCMS lets a Medicare Advantage plan use AI to help with coverage decisions. Each decision must rest on the member's own record and the plan's published criteria, and a physician or other qualified clinician must review any medical necessity denial before it goes out. Here is what to ask a vendor. · 5 min read
 Guide · Data qualityAI-ready data checklist for regulated teamsTwenty-eight checks to run against the data an AI process will read, before it goes live and at set intervals after. Grouped by stage, from sources and owners to documents, mapping and run-time checks, each with why it matters to an examiner and how to test it. · updated November 18, 2026 · 8 min read
 Article · GovernanceBusiness rules or AI guardrails? Why regulated work needs bothGuardrails filter what an AI model takes in and says. Business rules check what the work itself must satisfy. In regulated work you need both, plus a model's judgment for the messy parts. What each one catches, a worked example, and what to ask a vendor. · updated November 18, 2026 · 12 min read
See Phylax on one of your workflows.
Every project starts with one workflow your people know well, measured against what it costs you today.