

Inovagio SecretsSecrets and keys
Keep every credential sealed, scoped and rotated.
Holds credentials encrypted and gives each service only what it needs: configuration names a secret, never holds it.
We’ll spend 30 minutes with you on one of your workflows, and you don’t need to share any data.
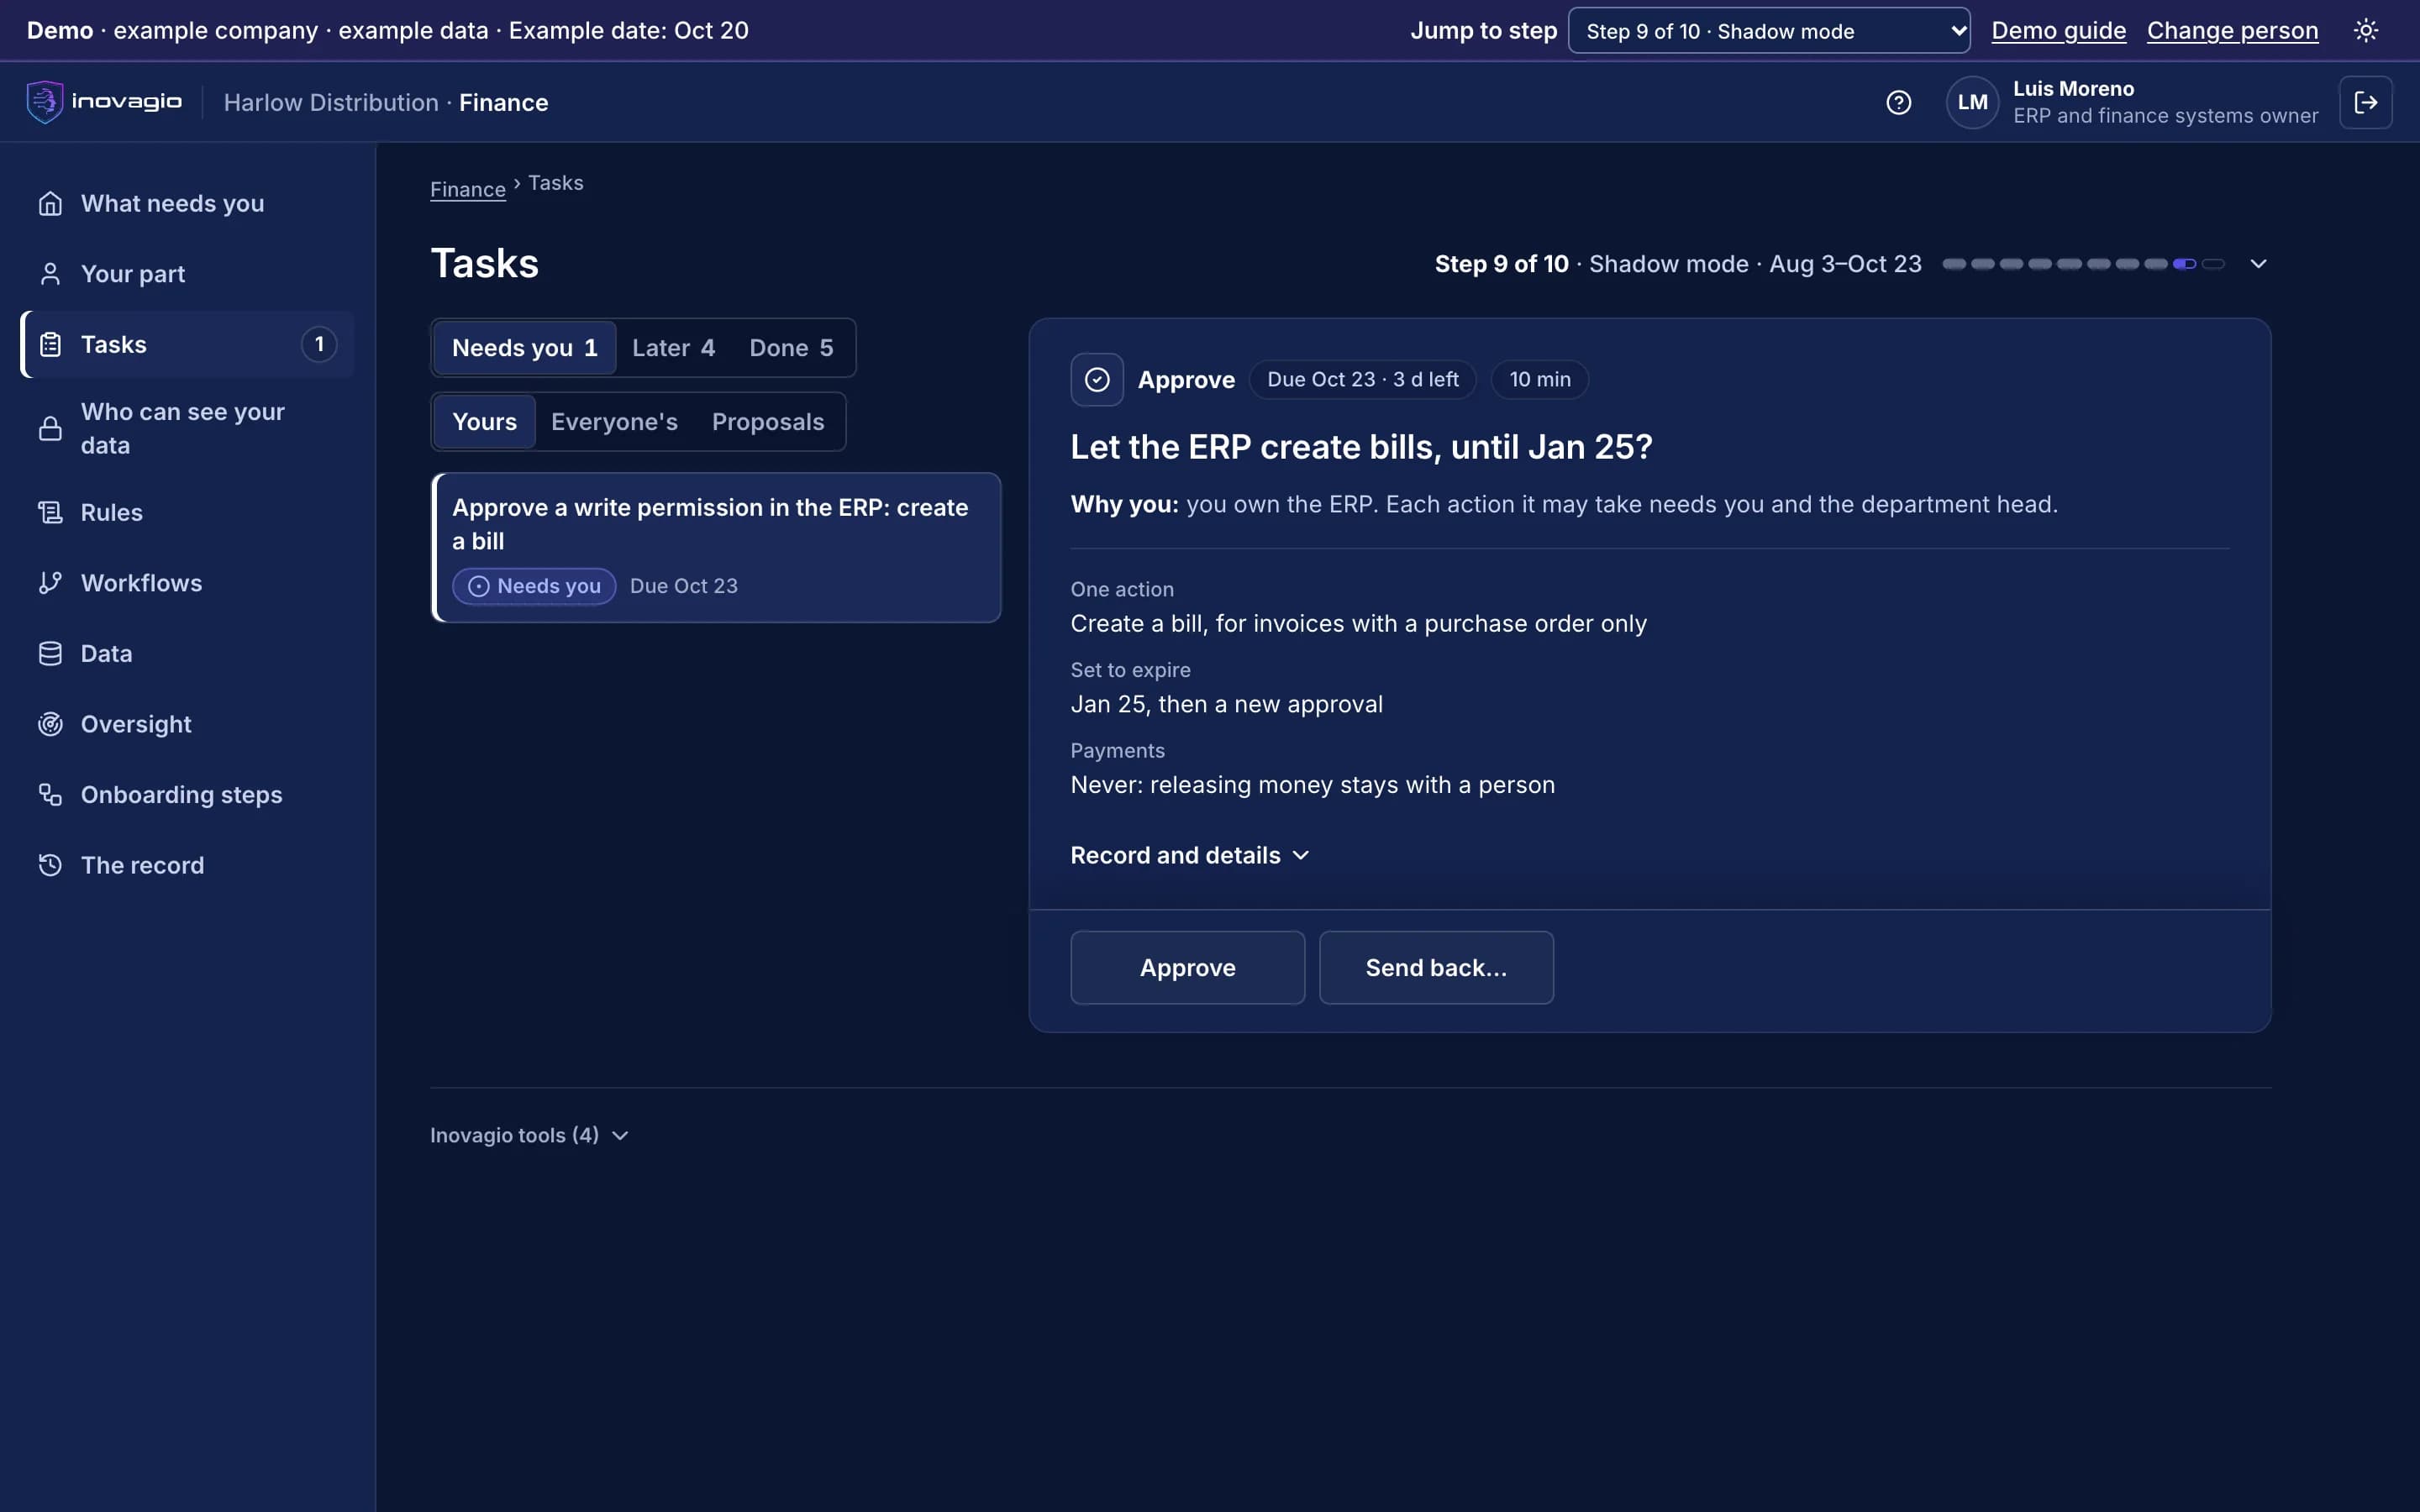
Where Inovagio Secrets works
Holds every credential sealed and scoped (Inovagio Secrets). These are the onboarding steps it works in, from your first decision to live work.
What Inovagio Secrets does
Inovagio Secrets is Inovagio’s secrets server: it holds service credentials and application secrets encrypted at rest, unseals from the operating system’s credential store, and gives each service only the secrets it is granted, so no credential sits in a config file, a command line or a process environment.
Referenced, never embedded
Configuration carries vault:// references that resolve at start, and a reference that does not resolve stops the service and names the reference.
Sealed by default
Secrets are encrypted at rest; while Inovagio Secrets is sealed, every secret route answers 503 and the key and cache are dropped from memory.
Unsealed from the OS store
The unseal key lives in the operating system’s credential store, and Inovagio Secrets recovers on its own once that store unlocks.
Recovery without loss
A recovery key shown once and optionally split into shares, envelope encryption and an audited key export mean losing one key does not lose every secret.
Scoped, expiring tokens
Service tokens carry policies, allowed paths and a lifetime, with lookup, renewal and revocation.
Rotation without restarts
Rotate a secret, or generate one from cryptographically secure random bytes, and dependent services pick up the new value without a platform restart.
A dedicated credential channel
Each service receives only its granted credentials over the platform’s credential channel, never through environment variables.
Brute-force lockout
Repeated failed tokens or unseal attempts lock out their source.
Every access audited
Reads, writes, rotations and unseals produce audit records that reach Panoptes.
Inovagio Secrets at work
In the App at step 3: Map the work and connect, read-only.
- The ERP is reached through its own API: reuse first.
- View only: vendors, purchase orders, receipts and the ledger. Nothing writes.
- The owner puts the credential into Inovagio Secrets, and it is never shown again.
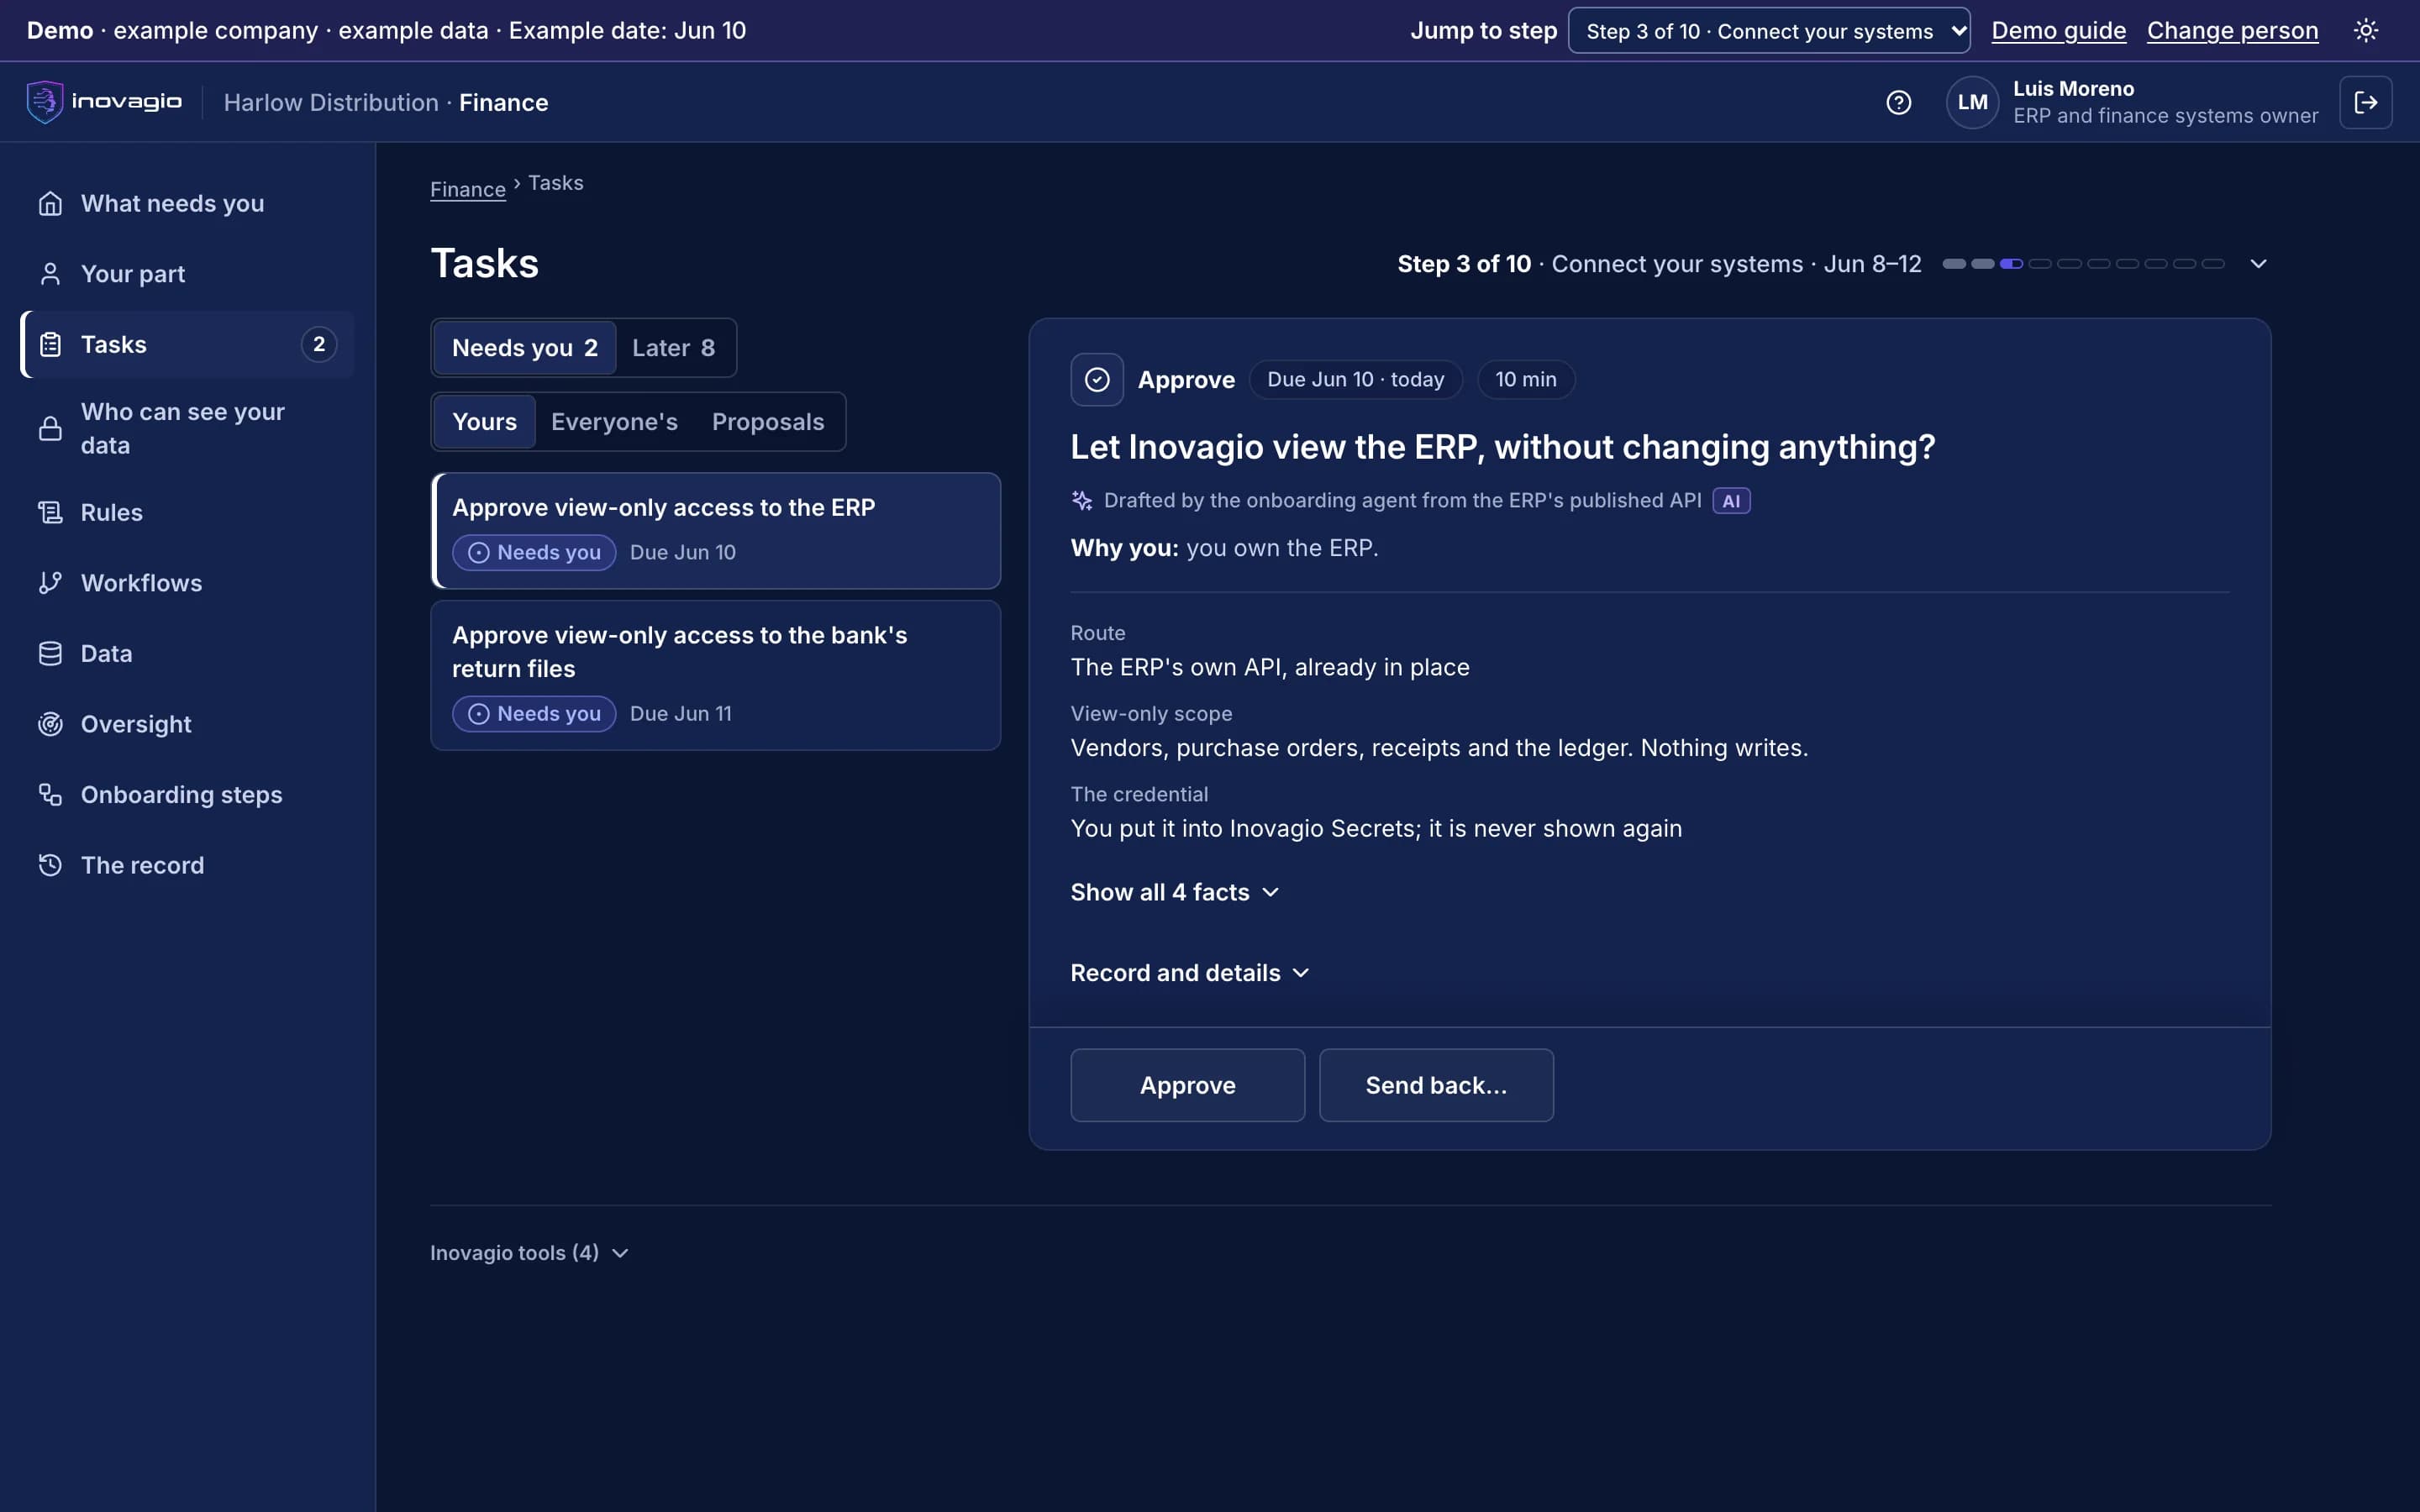
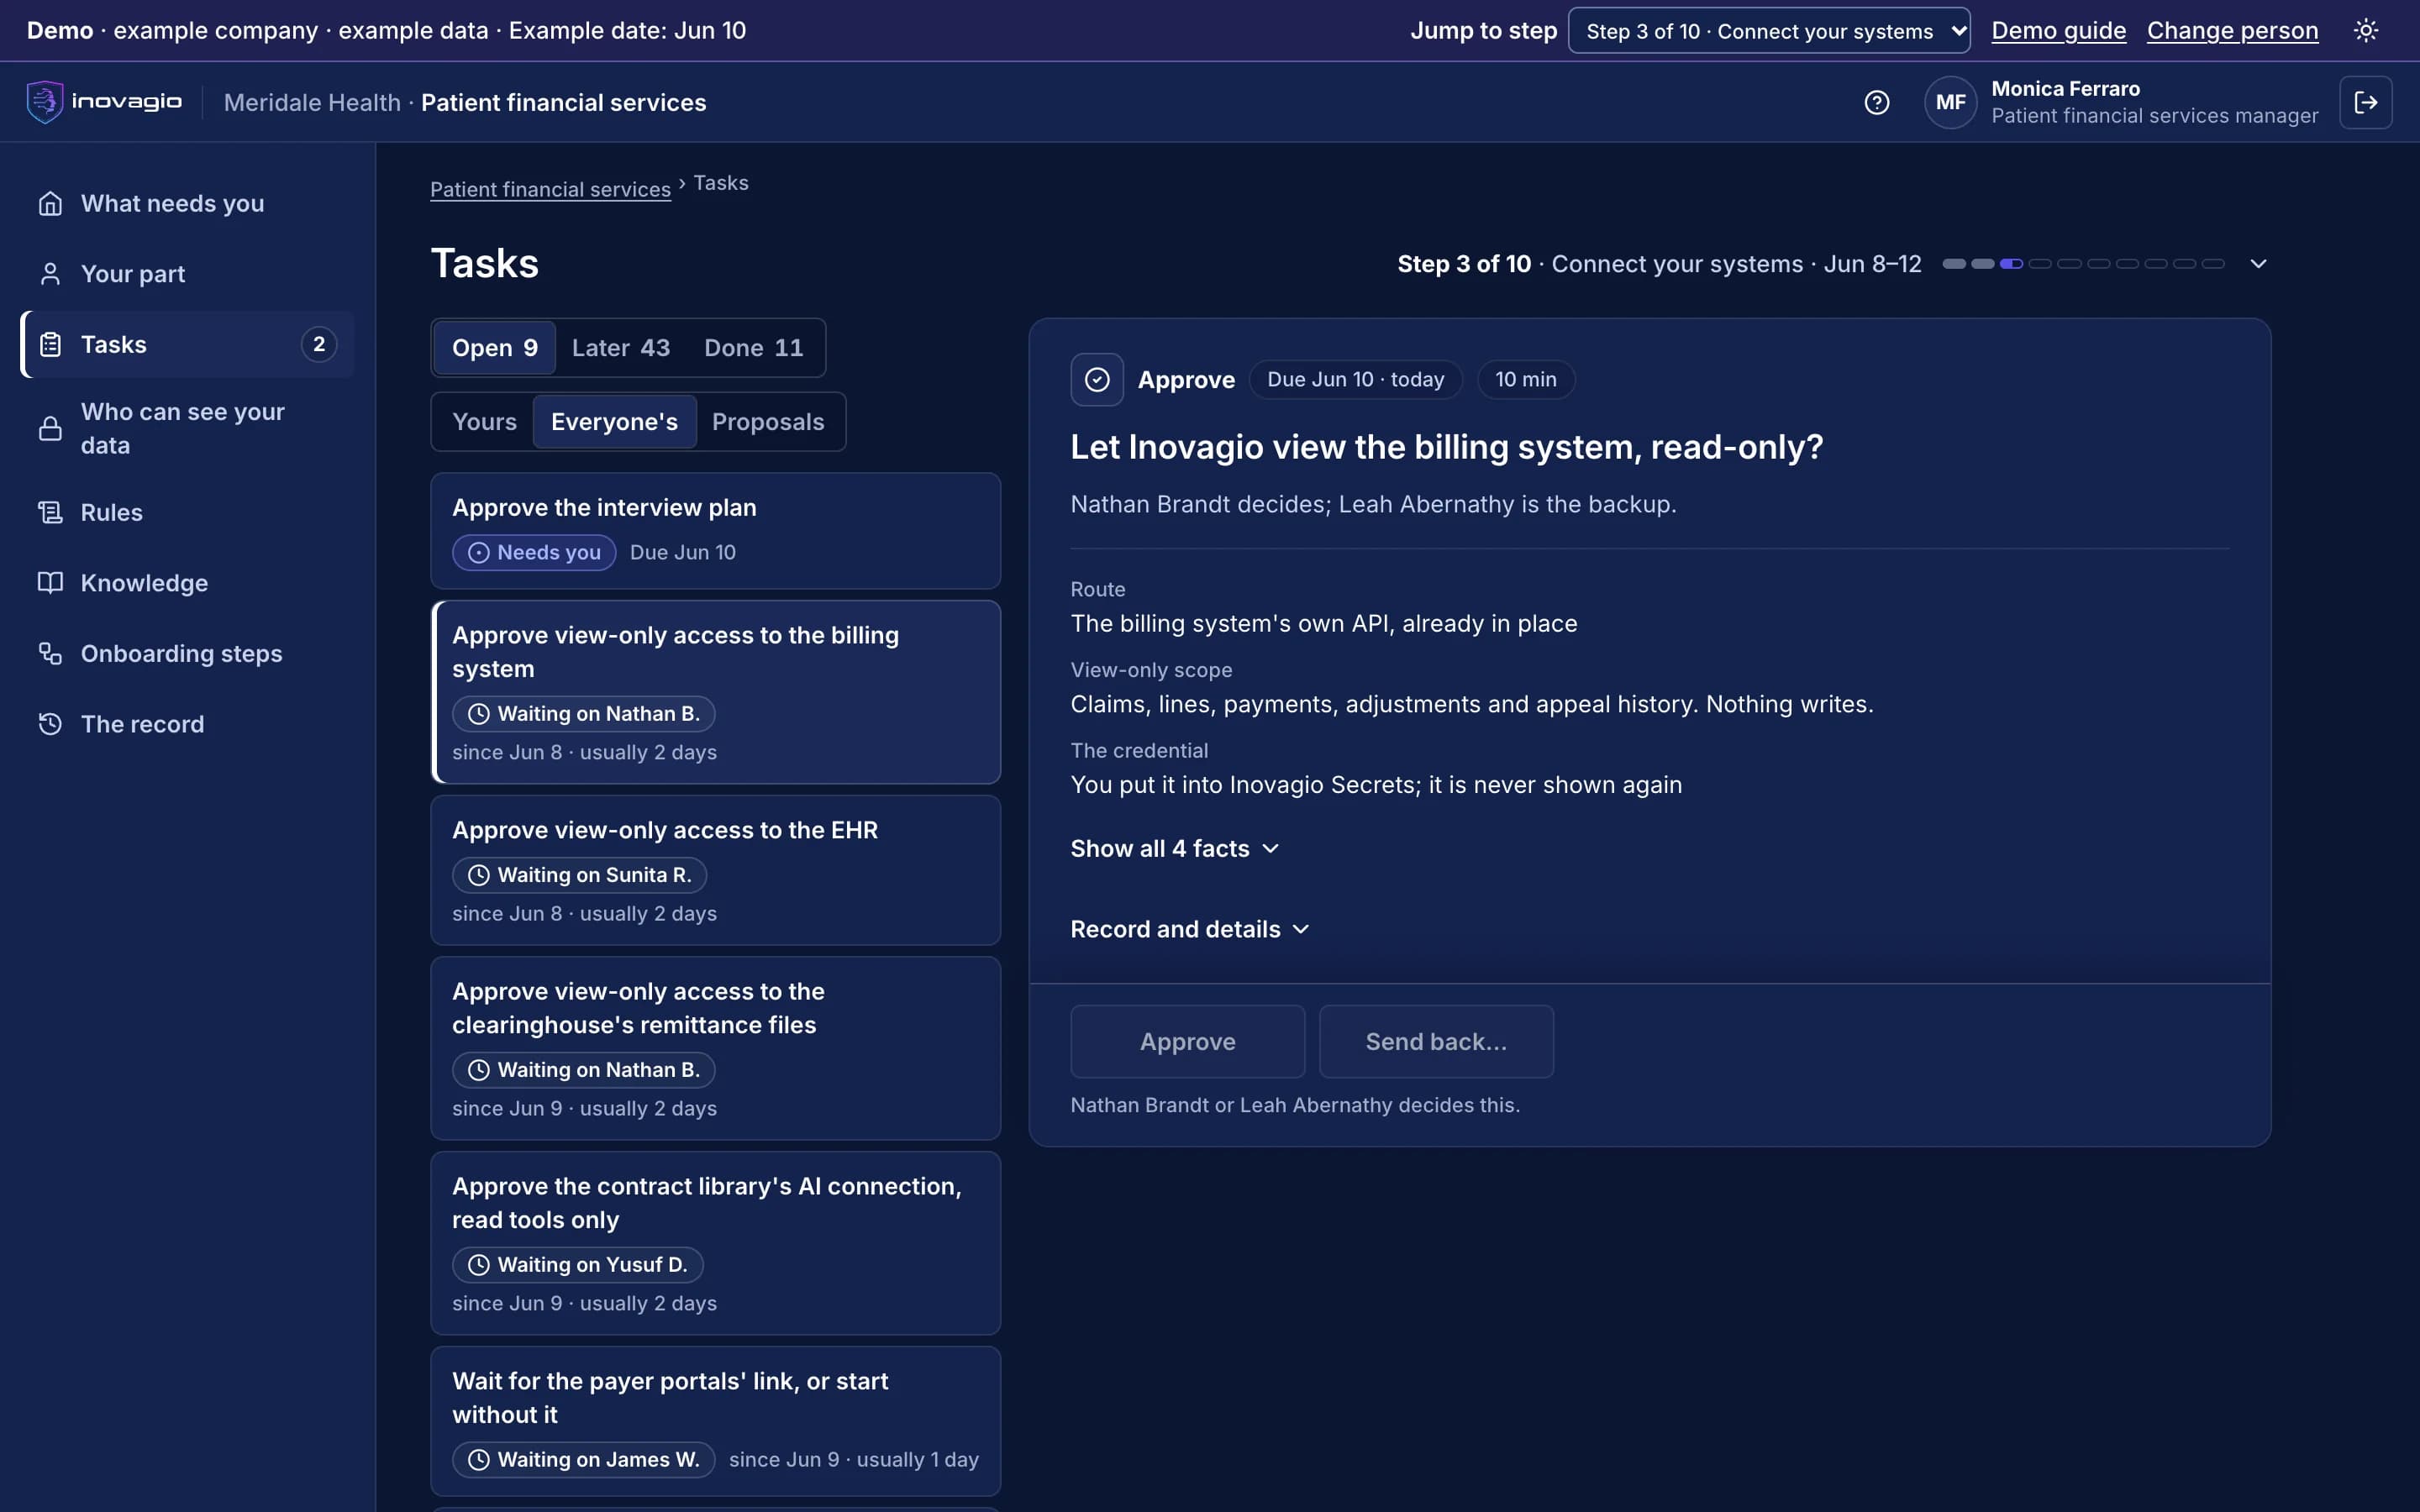
Inside Inovagio Secrets
The views Inovagio Secrets gives the people who run it, on sample data from Inovagio’s example companies.
- Synesis
- Virtual Employees
- Agent Harness
- Opsis
- Origin
- Phylax
- Operations
- Platform services
lending/loan-system/client-key
Rotates every 30 days · old and new versions overlap for 24 h
Handover
Schedule
- Every
- 30 days, at 14:00
- Overlap
- 24 h · both versions accepted
- Delivered to
- 4 consumers, no restarts
- Approval
- Automatic; early rotation needs a person
History
v15 · scheduled
14:004 consumers ready
v14 · rotated
30 days ago0 failed calls during handover
v13 · rotated
60 days ago0 failed calls during handover
v12 · rotated early
74 days agoAfter a role change, by a person
Consumers
- Connect · loan systemReady for v15
- Virtual Employees · commercial renewalsReady for v15
- Virtual Employees · loan servicingReady for v15
- Nexus · covenant agentReady for v15
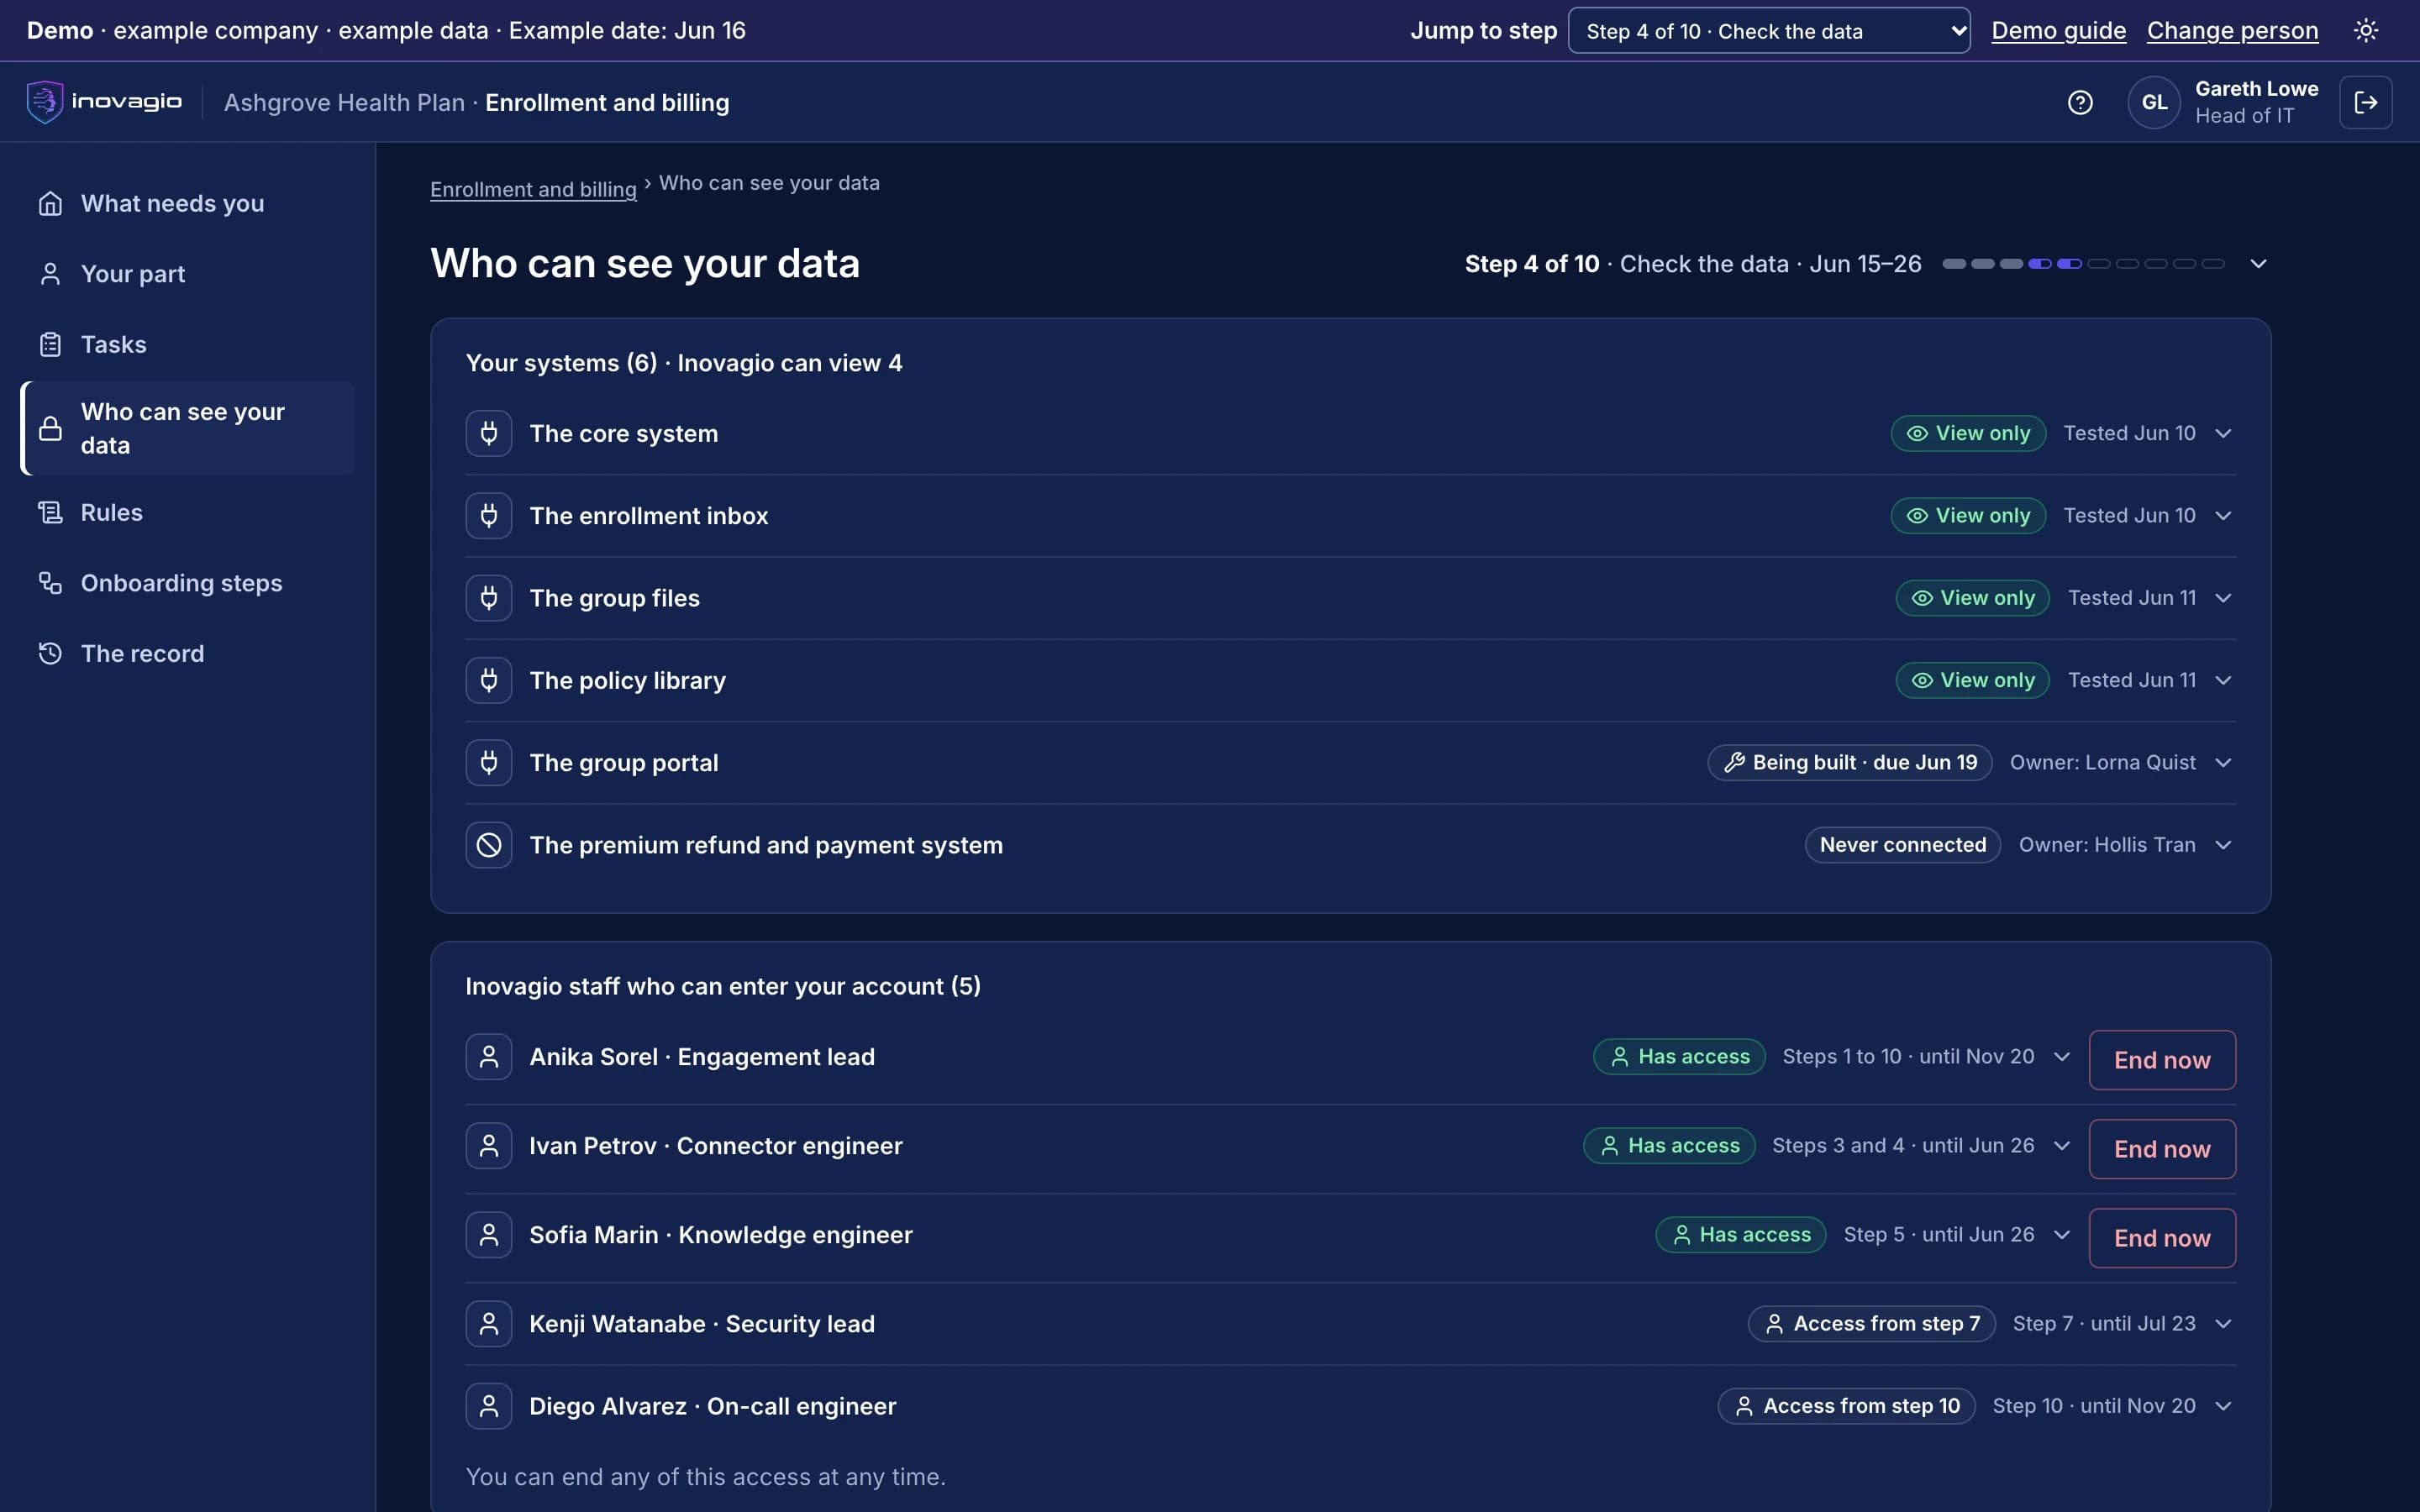
Inovagio Secrets › Credentials: a system’s owner approves view-only access and puts the credential into Inovagio Secrets, where it is never shown again. Sample data from Inovagio’s example companies.
Everything Inovagio Secrets does, by area.
Secrets
- Create, read, update and delete secrets by path
- List keys at a path
- Rotate a secret in place
- Generate a secret from secure random bytes
- Seal and unseal
- Health that reports seal status and the reason
Access
- Policy-scoped service tokens
- Token lifetime, lookup, renewal and revocation
- Path-scoped grants for each service
- Lockout on repeated failures
- Loopback binding by default
Keys and recovery
- AES-256-GCM encryption at rest with an Argon2id-derived key
- Unseal key in the macOS, Windows or Linux credential store
- Pluggable seal providers
- One-time recovery key with optional secret sharing
- Envelope encryption and audited key export
- Automatic recovery when the credential store unlocks
Platform integration
- vault:// references for TLS certificates, keys and admin credentials
- A build gate that every secret setting resolves or is refused
- Started first, with a health and unseal gate, before services that need it
- Credentials for sign-in admin, threat defense and telemetry delivered as grants
What Inovagio Secrets replaces
Inovagio Secrets does the work of these, inside one platform with one identity, one policy and one record:
- Secrets manager
- Credentials in config files and environment variables
- Shared service passwords
- Hand-run credential rotation
The controls Inovagio Secrets brings
Every Inovagio product keeps the same five commitments, because regulated work needs all five at once.
Security
Secrets are encrypted and scoped to the task that needs them, and every access is recorded.
Governance
Access to every secret follows policy.
On the record
Every read and change of a secret is recorded.
Monitoring
Seal state and access appear in Panoptes.
Cost per task
One secrets service for every product instead of one per system.
Inovagio Secrets in your industry
Every industry runs the same ten steps, so Inovagio Secrets does the same job in each, on that industry’s own work.
- Financial servicesBanks, credit unions, lenders and insurersWorked example: Alder Ridge Community Bank · Example company
- Healthcare providersHealth systems, hospitals and physician groupsWorked example: Meridale Health · Example company
- Health plansMedicare Advantage, Medicaid and commercial plansWorked example: Ashgrove Health Plan · Example company
- LegalLaw firms and in-house legal teamsWorked example: Calloway Finch · Example company
- GovernmentState, county and city agenciesWorked example: City of Larkhaven · Example company
- DefenseDefense contractors and their suppliersWorked example: Keelstone Aerospace · Example company
- Finance operationsFinance teams in any industry
For developers: Inovagio Secrets at a glance
- API
- Versioned REST API for health, seal and unseal, tokens, and reading, writing, rotating and generating secrets
- Encryption at rest
- AES-256-GCM; master key derived with Argon2id
- Unseal
- OS credential store (macOS, Windows, Linux) through a seal-provider port
- Recovery
- One-time recovery key, optionally split with Shamir secret sharing
- Audit
- Every access recorded and exported to Panoptes over OpenTelemetry
- Platforms
- macOS, Linux and Windows servers
Inovagio Secrets in the platform.
Where Inovagio Secrets fits
One platformAgent HarnessAgent harness
Inovagio CLIInovagio DesktopWeb ChatInovagio SDK
OpsisExperience layer
FolioMorphe
Virtual EmployeesVirtual Employee layer
NexusErgon
SynesisKnowledge layer
PerceptionMNEMOS
OriginModel layer
Inference ServerForge
Phylax (this layer)Trust layer
AuthInovagio Secrets (this product)Guard
OperationsOperations
PanoptesArchon
Platform servicesPlatform services
ServerAPI ManagementConnect
Further reading
Guides and posts on Inovagio Secrets
See Inovagio Secrets on one of your workflows.
Every project starts with one workflow your people know well, measured against what it costs you today.